Kaspersky researchers have discovered a sophisticated, updated version of the macOS infostealer known as MacSync. First emerging in 2024–2025 as a variant of the AMOS stealer, the malware has undergone a significant transformation. This latest version, spotted in September 2026, uses a new complex infection chain and delivers an infostealer and a backdoor to the victim’s device, compromising credentials, different types of user data, and crypto assets.
The attack begins with a malicious file ending up on a user’s device – this may be a result of the user downloading the malware disguised as a certain application (a document sharing app, crypto wallet app or other apps). This triggers a series of further malicious downloads and manipulations on the device. In some cases, one of the malicious downloads in the attack sequence is hosted in a public iCloud calendar entry in *.ics format. As a result of the infection, the core MacSync malware components are installed: an infostealer and a backdoor.
When launched, the infostealer appears as an application that the user thought they had downloaded. It prompts the user to enter the password for the administrator’s account. After the password is entered, a notification is displayed saying that the app “is damaged,” suggesting moving it to the bin – a technique intended to distract the user. The stealer collects web browser data (browsing history, cookies, saved credentials), data from crypto wallet apps, Telegram messenger data, the device’s login and password, and the Keychain file. It also collects the list of installed apps and the device’s model and hardware data, SSH, ZSH configs and other data.
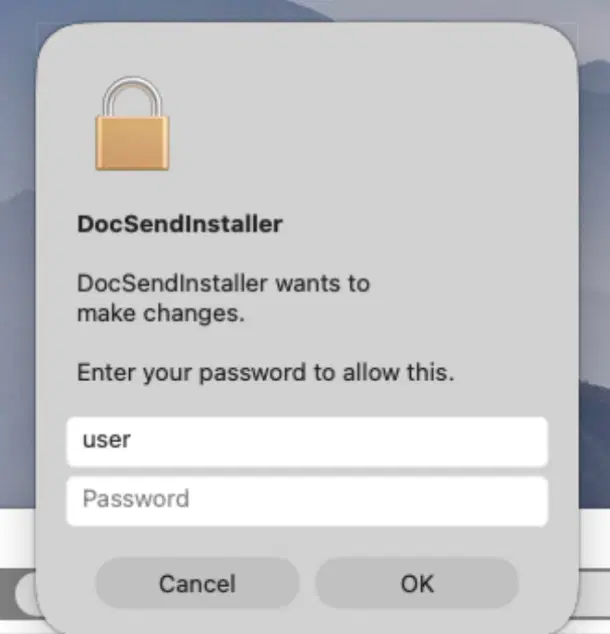
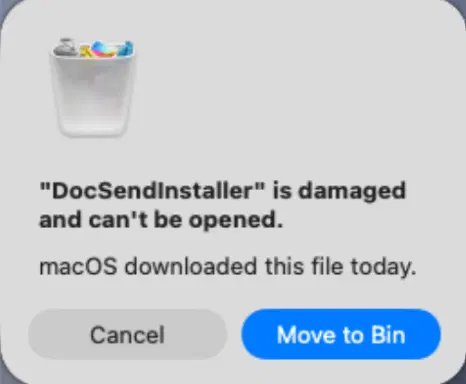 Fake
notifications used by the infostealer
Another MacSync component – the backdoor – is disguised as the legitimate Finder app and grants attackers access to the user’s data. Specifically, through this backdoor the attackers can remotely deploy modified add-ons in the user’s web browser (most likely to replace crypto wallet extensions with malicious ones), replace the legitimate Ledger crypto wallet app with a malicious clone, collect various system information or specific user files, and possibly execute arbitrary code for other purposes.
“The newly discovered version of the MacSync infostealer differs significantly from its previous versions, introducing new features and making the infection chain more complex. Threat actors are also actively developing social engineering techniques that serve as the initial access window to the victim’s device, and it is important to stay vigilant when installing new applications, especially if the app developer is not trusted. We recommend to always check if the app you are downloading or installing is from the original developer, verifying its legitimacy via trusted sources. Your administrator password is the key protecting the most sensitive data and credentials on the device, and users should be alert when applications ask for it,” comments Sergey Puzan, security expert at Kaspersky.
Kaspersky security solutions successfully detect and neutralise threats associated with the MacSync malware family.
More detailed information on the updated MacSync malware will be available on Securelist.com in the coming days.


